KeyForge AI
Identity Governance & Administration

Identity governance that decides, not just provisions.

Lifecycle, access requests, approvals, certifications and remediation on one platform — run standalone, or extend the IGA you already operate with risk intelligence and automated remediation.

Capabilities

The foundation of the identity programme

Lifecycle

Joiner, mover, leaver — and everything between

Transfers, contract extensions and sponsorship changes re-evaluate existing access, not just provision new access.
Access request

Preventive, not detective

Requests are simulated before provisioning. A grant that would complete a toxic combination is refused while it is still a request.
Approvals

Routed to the right owner

Approvals reach the manager, application owner or data owner with the risk context needed to decide, not just a role name.
Certification

Risk-based campaigns

Line items carry risk, usage history and peer comparison, so reviewers have a basis to revoke rather than approve everything.
Remediation

Surgical, with a rollback path

Lineage names the specific grant to remove, so remediation does not strip a whole role and break someone's job.
Audit

Evidence generated, not reconstructed

Every decision retains the rule, the signals, the approver and the outcome as a reproducible record.

Privileged & just-in-time access

Standing privilege, replaced by time-bound access

The highest-risk entitlements are the ones nobody needs every day. Hold them as eligibility, grant them for the task, and let them expire.

Eligibility

Eligible, not standing

Privileged roles are held as eligibility. Elevation is requested for a task, with a reason and a duration.
Time-bound

Expiry by default

Access granted for a window is withdrawn when the window closes — without a ticket to remember it.
Evidence

Every elevation recorded

Who elevated, why, for how long and what changed — retained alongside the approval that allowed it.

In the product

Everything open, ranked by what breaches first

Findings carry severity, SLA burn-down and the reviewer they were routed to — so the queue sorts by consequence rather than by application name.
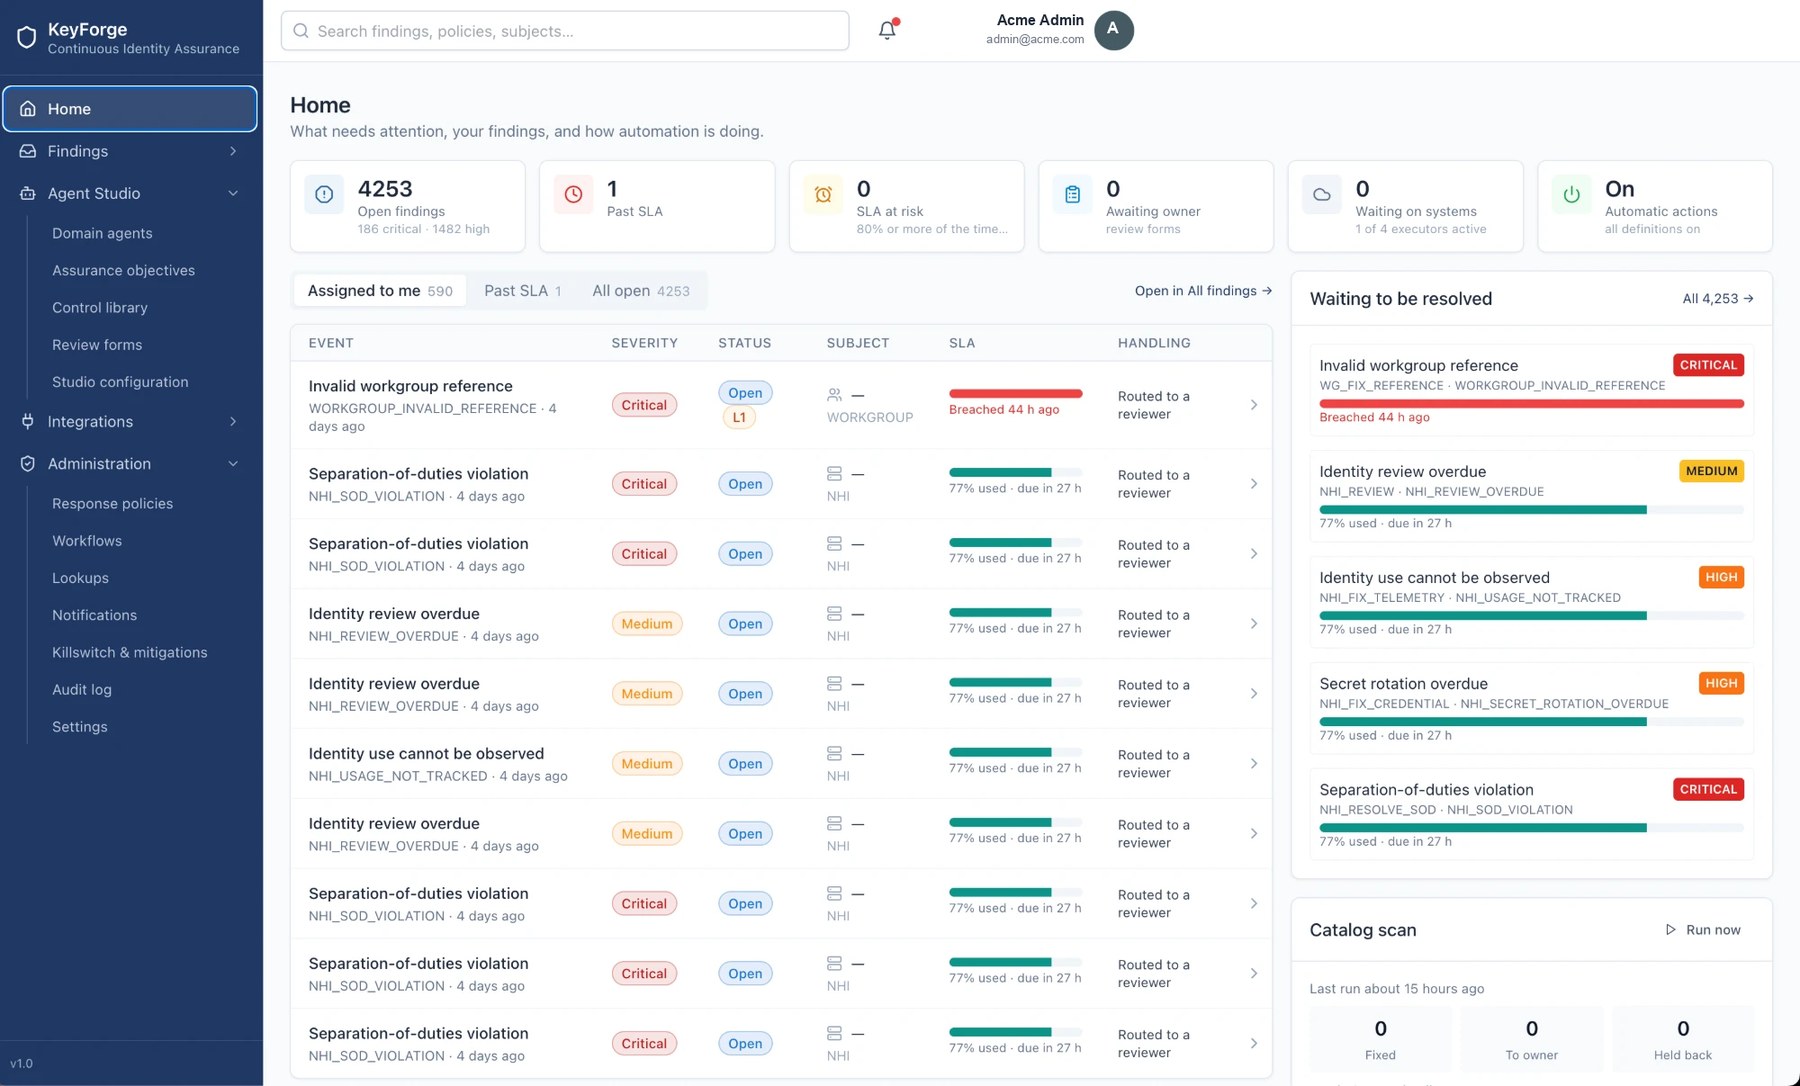
Findings dashboard showing open findings by severity, SLA progress and routing to reviewers
Findings — severity, SLA burn-down and routing

Application onboarding

Connect the estate in minutes, not days

Pre-built integrations cover the major ERP, directory, cloud and SaaS platforms. AI-based self-discovery connectors for REST and database sources bring the long tail of in-house applications into governance.
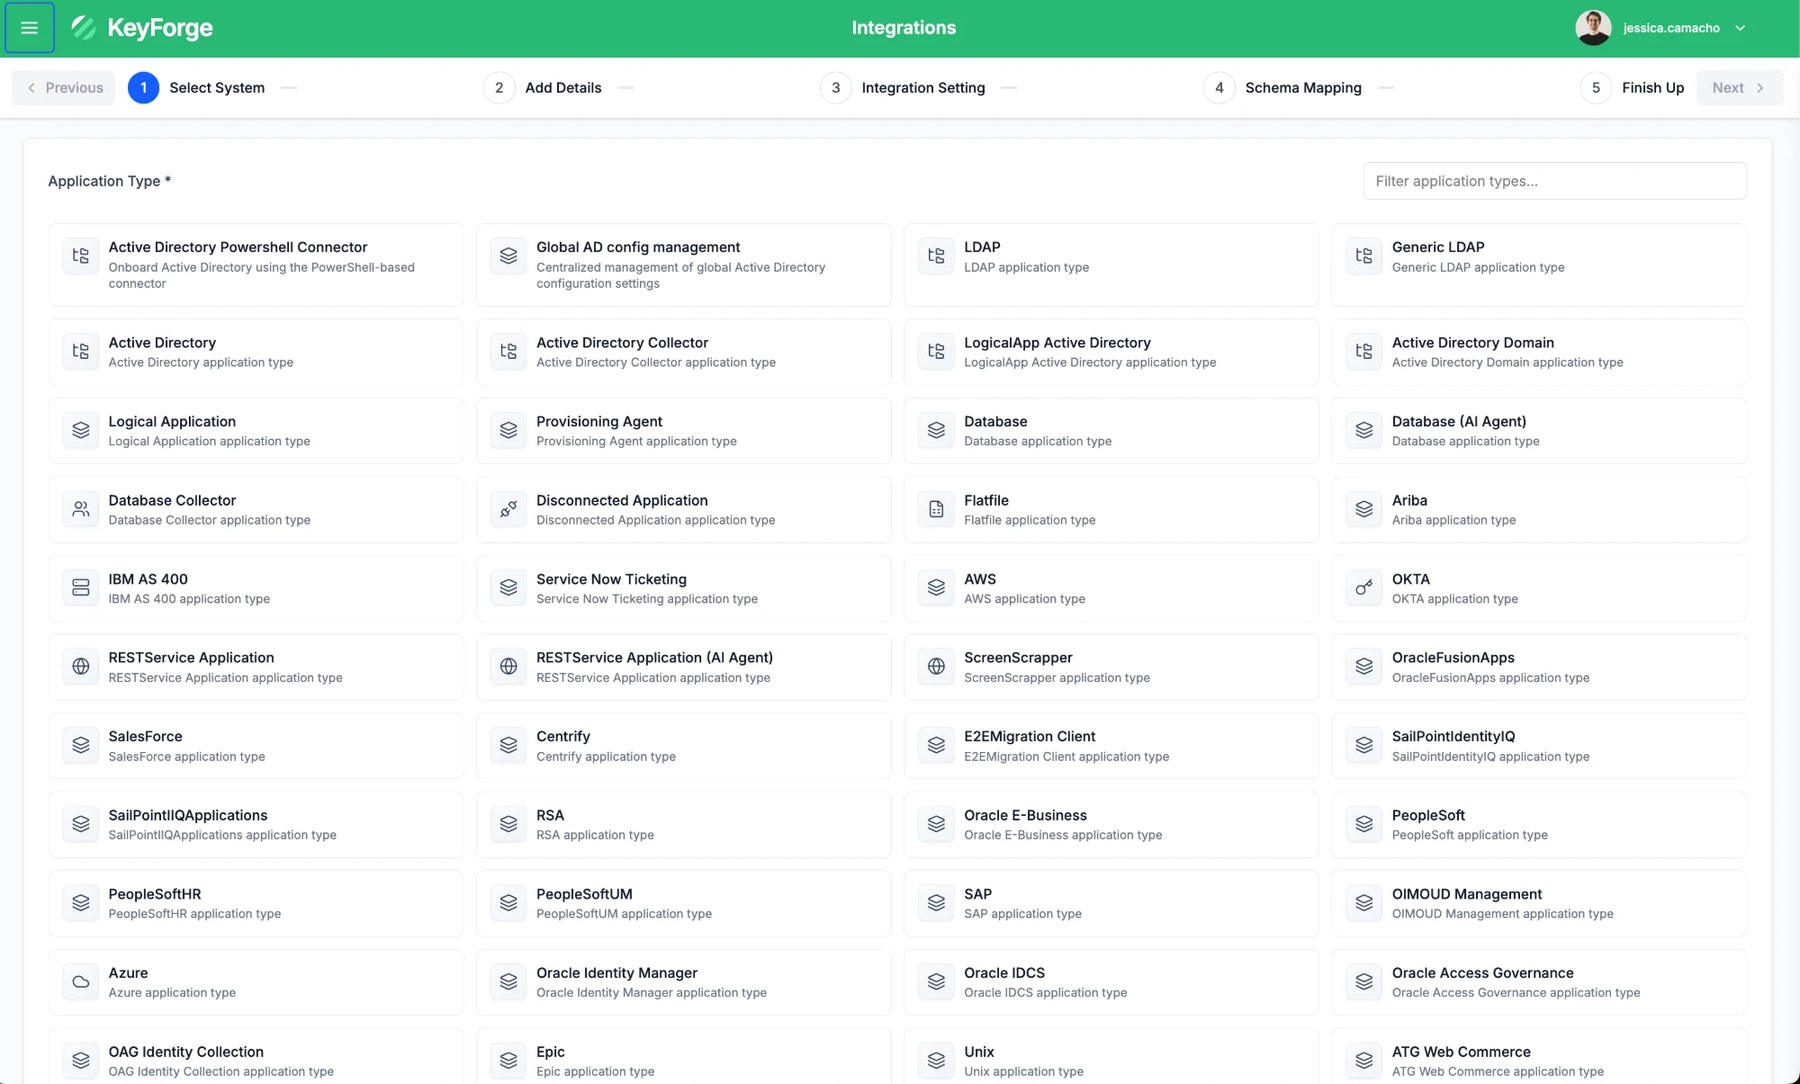
Integrations catalog listing pre-built connectors across ERP, directory, cloud and SaaS applications
Integrations catalog

Browse integrations →

Deployment

Standalone, or on top of what you own

KeyForge AI can operate as your primary IGA or extend an existing IGA investment such as SailPoint, Saviynt or Oracle with fine-grained risk analysis, continuous assurance and automated remediation. The choice depends on where your programme is today, not on what the platform can do.

Related capability: Access reviews & micro-certifications →

Humans · machines · AI agents

One lifecycle for every identity type

People

Joiner, mover and leaver events, access requests and risk-based certifications for employees and contractors.

Non-human identities

Service accounts, API keys and certificates given a named owner, a purpose, a rotation schedule and an expiry — and certified alongside people.

NHI security
AI agents

AI agents registered with an owner and delegated authority, scoped, expired on time and reviewed in the same campaigns.

Agentic AI security

The portfolio

Built on the same foundation

See it against your own entitlement model.

Book a technical demo, or score your programme in five minutes first.