KeyForge AI
Platform

One foundation under every product.

Each KeyForge AI product reads from the same identity graph, evaluates the same policies and writes to the same evidence store. Adding a product adds coverage — not another inventory to reconcile.

Shared platform foundation

Six components, shared by all five products

Identity Graph

People, machines and agents in one model

Identities, accounts, roles, privileges and data scopes from every connected system, resolved to effective access with the path that grants it.
Policy Engine

Versioned, readable rules

SoD, sensitivity, lifecycle and delegation policies stated in plain language and evaluated deterministically, so every outcome names its rule.
Risk Analytics

Scored with the evidence attached

Severity, blast radius, usage and peer comparison combined into a score a reviewer can interrogate rather than accept on faith.
Workflows

Requests, reviews and remediation

Approvals, micro-certifications, mitigations and revocations routed to the right owner with an SLA.
Connectors

Pre-built and AI-discovered

Pre-built integrations for major ERP, directory, cloud and SaaS platforms, with AI-based self-discovery connectors for REST and database sources.
Audit Evidence

Generated at the moment of decision

Every detection, decision and remediation retained as an immutable record that can be replayed for an auditor.
The reasoning layer

Continuous Identity Reasoning

The architectural core: signals are evaluated against identity, intent, context, risk and policy, and every decision carries the evidence that produced it. Deterministic rules come first; AI-powered recommendations assist the reviewer without replacing the rule.

Read the architecture

Policy & authorization governance

Cloud policy, governed like access

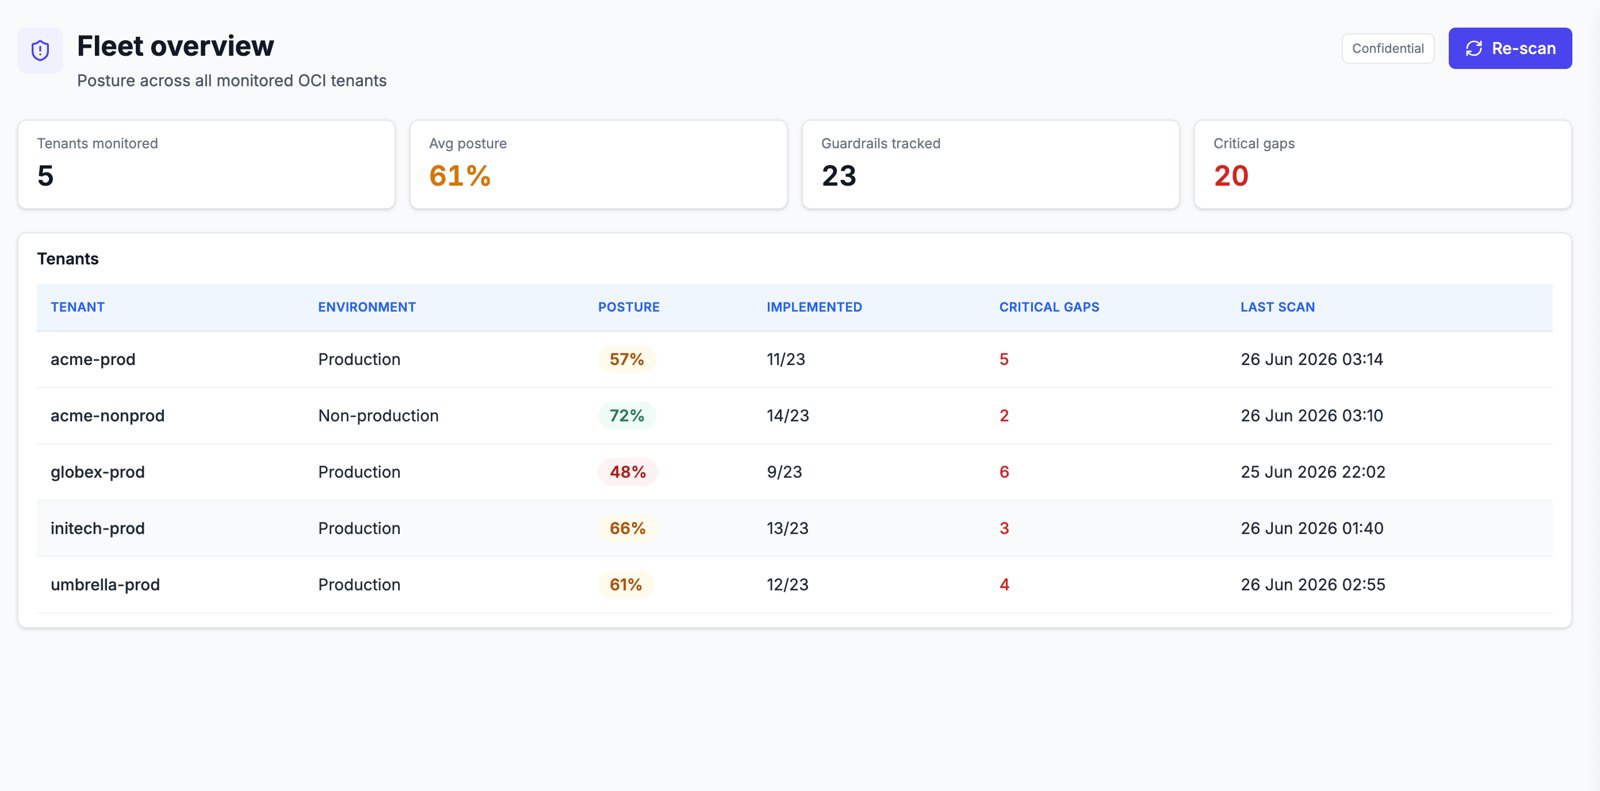
Authorization policy is access in another form. OCI IAM policies and guardrails are tracked as posture across tenants, with drift detected against the approved baseline and gaps routed for remediation.

Fleet overview of monitored OCI tenants showing posture percentage, implemented guardrails and critical gaps per tenant
OCI policy posture — guardrails and critical gaps across tenants

Deployment

Standalone, or alongside the IGA you run

Standalone

KeyForge AI as the primary IGA

Lifecycle, requests, certifications, application access governance and assurance on one platform.
Alongside

Extending SailPoint, Saviynt or Oracle

Your IGA keeps provisioning. KeyForge AI adds fine-grained risk, continuous assurance, NHI and agent governance on top.
Assessments start read-only: connectors collect entitlements and configuration without writing to the target systems, and remediation is enabled only when you choose to turn it on.

Security

How the platform treats your data

Isolation

Tenant-isolated by design

Each customer's data is separated at the data layer, so one tenant's queries cannot reach another's records.
Least privilege

Read-only until you decide

Collection uses scoped, read-only service credentials. Write access for remediation is a separate, explicit grant.
Evidence

Every action attributable

Administrative actions, decisions and remediations are recorded with the actor, the reason and the time.

Security questionnaires and architecture details are available on request — contact us.

Products

Built on this foundation

See the platform against your own estate.

Book a technical demo, or start with a read-only assessment.