KeyForge AI
Identity Governance

Identity governance that decides, not just provisions.

The leading IGA platforms move access through an enterprise efficiently. The judgement behind each decision — who should hold it, under what conditions, for how long — is still largely manual. That is the part we automate.

Capabilities

What the platform governs

Access request

Preventive, not detective

Requests are simulated before provisioning. A grant that would complete a toxic combination is refused while it is still a request.
Lifecycle

Joiner, mover, leaver — and everything between

Transfers, contract extensions and sponsorship changes re-evaluate existing access, not just provision new access.
Certification

Risk-based campaigns

Line items carry risk, usage history and peer comparison, so reviewers have a basis to revoke rather than approve everything.
Risk & SoD

Fine-grained, cross-application

Conflicts evaluated at the privilege level and across systems, with the inheritance path that caused them.
Remediation

Surgical, with a rollback path

Lineage names the specific grant to remove, so remediation does not strip a whole role and break someone's job.
Audit

Evidence generated, not reconstructed

Every decision retains the rule, the signals, the approver and the outcome as a reproducible record.

How it works

Signals in. Evidence out.

  1. 1

    Signals

    Entitlement, HR and usage events arrive from the systems you already run.

  2. 2

    Reasoning

    Risk, peers, blast radius and policy evaluated against a versioned rule.

  3. 3

    Decision

    Revoke, approve with mitigation, accept risk or dismiss — signed.

  4. 4

    Remediation

    Executed against the target system, automatically or by a reviewer.

  5. 5

    Evidence

    Every transition written to an immutable audit record.

In the product

Everything open, ranked by what breaches first

Findings carry severity, SLA burn-down and the reviewer they were routed to — so the queue sorts by consequence rather than by application name.
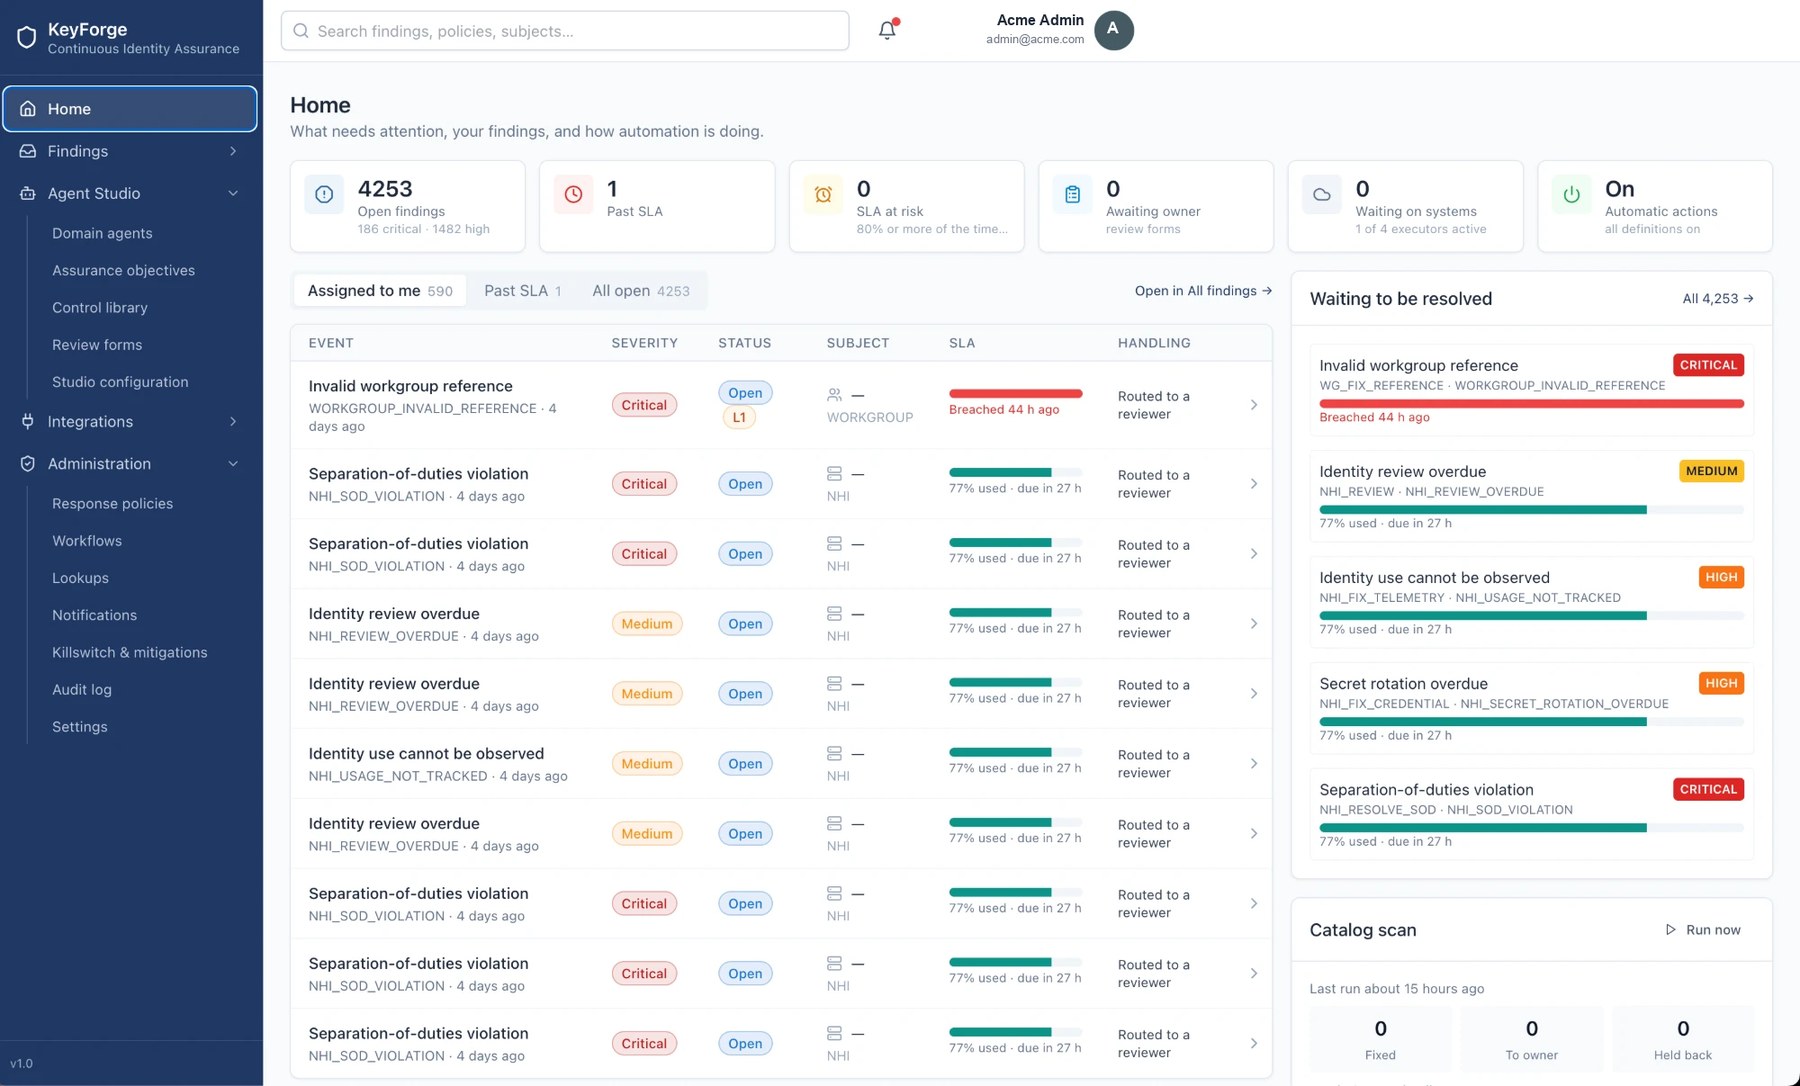
Findings dashboard showing open findings by severity, SLA progress and routing to reviewers
Findings — severity, SLA burn-down and routing

Detection coverage

Signal families, and what is live today

A detector becomes a control once an agent can resolve the facts it needs. The library states plainly which families are covered and which still need a connector — so coverage is a fact, not a claim.
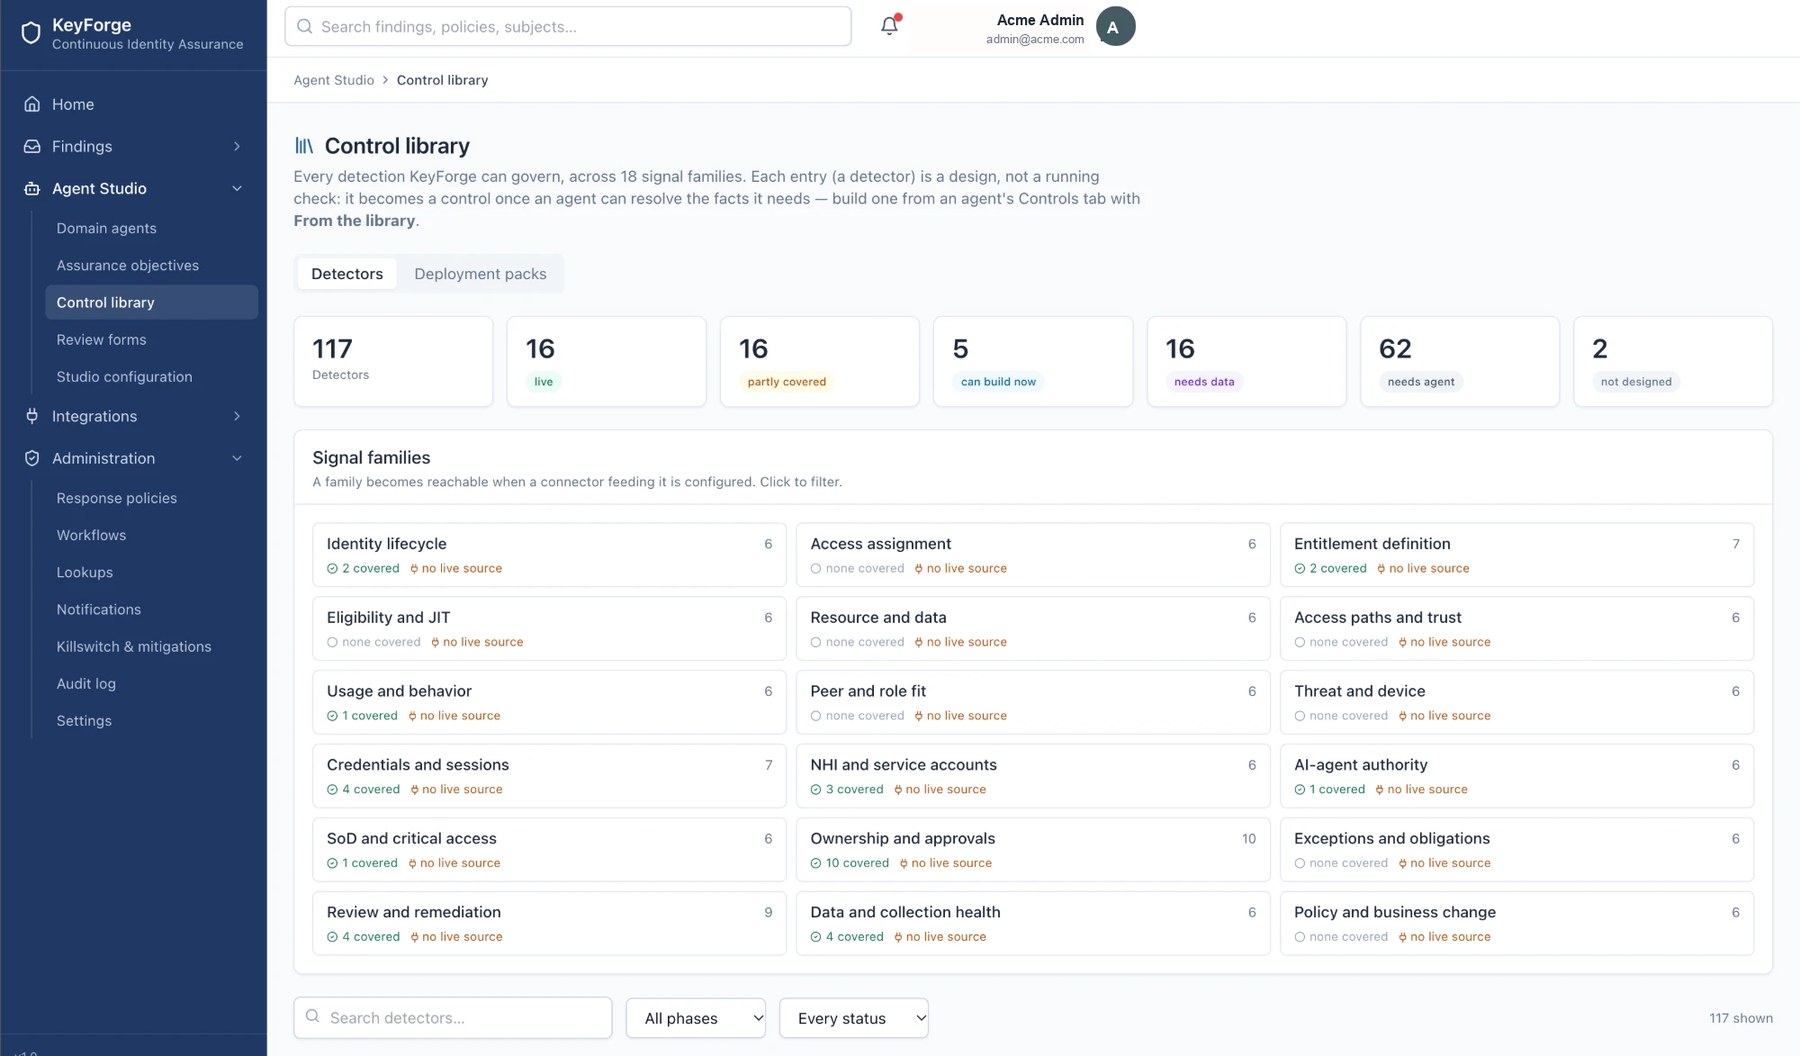
Control library showing detectors grouped into signal families with coverage status
Control library — signal families and live coverage

Deployment

Standalone, or on top of what you own

KeyForge AI is a continuous identity governance and assurance platform that can operate standalone or extend existing IGA investments with policy-driven reasoning, risk intelligence and automated remediation. Running SailPoint or Saviynt is a reason to deploy the reasoning layer, not a reason to replace the platform.

See it against your own entitlement model.

Book a technical demo, or score your programme in five minutes first.